DevSecOps Services That Fit Your Product By NextGenSoft
Most teams don’t fail because of bad code. They fail because security comes in too late. Our services embed security into your architecture, pipelines, and cloud environments from the start. Issues are caught early, not during release week.
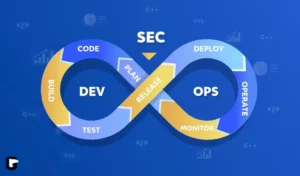
We begin by reviewing how your product is built and deployed today. Our DevSecOps consulting services design secure CI/CD pipelines and automated security checks. Every build and deployment follows the same rules, without manual intervention.
This removes release risk and reduces production failures. Teams move faster without cutting corners. With our DevSecOps managed services, security becomes part of delivery, not a blocker to it.
Why Security is Essential in DevSecOps?
Early Risk Detection
Now identify and fix security during development, not after the release. With DevOpsSec Services, automated scanning and continuous testing catch the issue early, while it is still easy to fix.
Predictable Release Cycles
When deployments depend on manual steps and scattered tools, every release is risky. DevSecOps Services bring consistency, same checks, same controls, same outcome, so you know exactly what’s going live.
Faster Time to Market
Security shouldn’t slow engineers down or sit on their shoulders. DevSecOps Services automate enforcement so teams can focus on building, not double-guessing every commit.
Built-In Compliance
Instead of scrambling for audits or evidence, controls are already in place. DevSecOps Services make compliance continuous and repeatable, not something you “prepare for.”
End-to-End Delivery Visibility
You can trace changes, from code to deployment to runtime, without piecing things together. That clarity alone saves hours during incidents and reviews.
Lower Operational Costs
Security flaws and environmental issues are cheapest when caught early. This service reduce rework, emergency patches, and long-term operational drag. Especially when supported through structured DevSecOps managed services rather than ad-hoc security fixes.
Challenges in DevSecOps
However, it is crucial to establish an efficienct and versatile DevSecOps strategy, but this may affect the seamless implementation and workflow of the organization.
Security Delays Releases at the Final Stage
When security is added at the end, issues surface right before release. Teams either delay launches or push risky code into production, both of which hurt the business.
Automation Fails to Improve Delivery Speed
CI/CD alone doesn’t fix everything. Without DevSecOps, pipelines move fast until security reviews stop them, creating bottlenecks no one planned for.
Operational Incidents Become More Frequent
Hidden vulnerabilities make it into production. Over time, this leads to frequent patches, hotfixes, and unplanned downtime that drains engineering focus.
Compliance Relies on Manual Effort
Audits and compliance checks rely on documents and manual reviews. This increases effort, errors, and stress, especially as the product scales.
Delivery Teams Remain Disconnected
Development ships features, security flags, risks, and operations deal with failures. Without DevSecOps, no one owns the full delivery lifecycle.
Scaling the Product Becomes Risky
As traffic, data, and users grow, security gaps grow with them. What worked early starts breaking under real-world load and threats.
Security and Operations Costs Escalate
Fixing security issues after release is expensive. Teams spend more time on rework, incident response, and support instead of building new features.
Release Confidence Declines Over Time
Over time, teams lose trust in deployments. Every release feels risky, which slows decision-making and limits how fast the business can move.
The DevSecOps Standards We Follow
Process Before Automation
If your release process is messy, automating it just makes the mess faster. We first clean up how code moves from commit to production, then add security and automation where it makes sense.
Security Built Into Development
Security shouldn’t show up at the end and block a launch. We plug it into code commits, builds, and infrastructure changes so issues surface early, when they’re easier to fix.
Stable, Predictable Pipelines
Over-engineered pipelines fail under pressure. We design CI/CD pipelines that are easy to understand, easy to debug, and reliable during high-stakes releases.
Risk-Based Tool Selection
Every product has different risks. We select security and DevSecOps tools based on what your system actually needs, not what’s trending or overkill.
Resilient Release Design
Things break in real environments; that’s normal. We plan rollbacks, alerts, and recovery paths upfront so a bad release doesn’t turn into a business incident.
Long-Term Team Ownership
DevSecOps only works if your team understands it. We document decisions, explain why things are built a certain way, and make sure you’re not dependent on us after delivery.
Why NextGenSoft?
End-to-End Expertise
Partner with NextGenSoft, a global digital transformation company, and leverage our multi-cloud engineers’ abilities. As a trusted IT solutions provider, we build up secure inter-cloud networks, map native cloud services, and make vendor-agnostic methodologies to maximize esteem and minimize dangers.
Delivery Excellence
We rethink delivery excellence with optimized program lifecycles. From development to deployment, our digital transformation services and solutions ensure reliable, high-quality releases that enhance client satisfaction, as showcased in our Case Studies.
Flexible Hiring Model
NextGenSoft’s adaptable contracting models give access to talented IT service providers custom-fitted to your needs. Scale easily with agile assets for DevOps, guaranteeing consistent collaboration and venture victory.
Transparent Actions
Our commitment to straightforwardness builds belief and cultivates cooperation. As a leading digital transformation company in India, we ensure adjusted objectives, open communication, and compelling collaboration for shared success.
Security Tools
- SAST Tools
- DAST Tools
- SCA Tools
- IaC Security Tools
- SIEM Tools
- Secret Management Tools
- Pipeline Security Tools
- EDR Tools
- Threat Intelligence Tools
- CSPM Tools
- IAM Tools

Pranav Lakhani 
Abdullah Sheikh