OIDC vs SAML: Which SSO Protocol Should You Choose?
Kushal BaldevSeptember 29, 2026
Share this article


Let AI highlight what matters.
Most teams treat the OIDC vs. SAML question as a technology preference. Developers like OIDC because it’s JSON and modern. Security teams defend SAML because it’s what the enterprise already runs. Then the product ships, and the first large customer’s IT team asks for the protocol you didn’t build.
The better question is not “which protocol is better?” It is “Who has to connect to us? From what kind of app, and what does their identity provider already speak?”
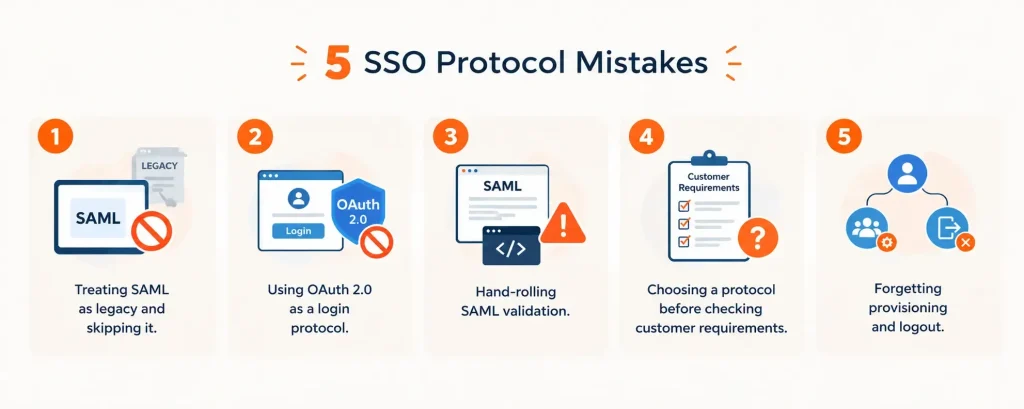
This guide covers what SAML and OIDC are, the real technical differences, and a practical framework for when to use SAML vs. OIDC. It also covers the mistakes that turn an SSO rollout into a rework project.
Both protocols do the same core job. A user signs in once with an identity provider (IdP), such as Okta, Microsoft Entra ID, or Google Workspace. The IdP then vouches for that user to an application (the service provider or relying party), so the user doesn’t need a separate password there.
Security Assertion Markup Language (SAML) 2.0 was ratified by OASIS in 2005. It was designed for browser-based web SSO in enterprises.
OpenID Connect was finalized by the OpenID Foundation in 2014. It is an identity layer built on top of OAuth 2.0.
A common confusion: OAuth 2.0 alone is an authorization framework. It lets an app access resources on a user’s behalf. It does not reliably tell the app who the user is. OIDC adds that authentication layer. “Login with OAuth” without OIDC is a known anti-pattern.
Read more: How to Enable Enterprise SSO with Auth0 and Azure AD (in 20 Minutes)
The biggest difference between SAML and OIDC is the environment each was built for. SAML assumes a browser and an enterprise web app. OIDC assumes a mix of web apps, native apps, and APIs. Here is an OIDC vs SAML comparison across the factors that matter in practice:
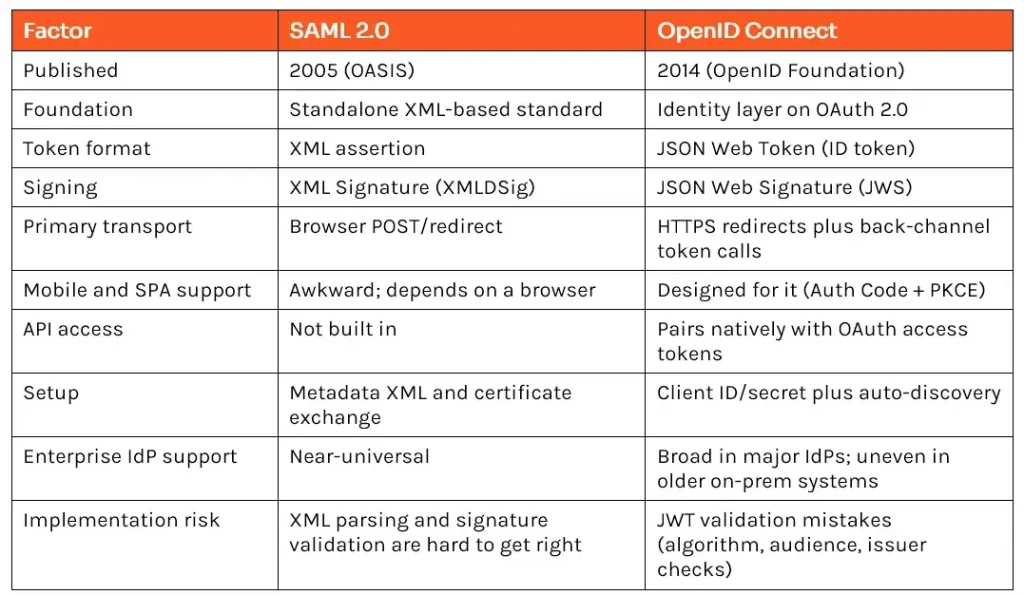
SAML’s XML assertions are verbose. They are also notoriously difficult to validate securely. XML Signature Wrapping attacks have repeatedly broken SAML libraries because the signed element and the element the app actually reads can differ. JWTs are smaller and easier to parse. However, OIDC implementations still fail when they skip checks on the signature algorithm, issuer, audience, or expiry.
OWASP SAML Security Cheat Sheet: https://cheatsheetseries.owasp.org/cheatsheets/SAML_Security_Cheat_Sheet.html
SAML defines Single Logout, but it is widely considered brittle in real deployments. OIDC has separate specifications for RP-initiated, front-channel, and back-channel logout. These are more flexible, but IDP support for them varies. With either protocol, test logout explicitly. It is the part teams most often assume will “just work.”
Neither SAML nor OIDC handles user provisioning and deprovisioning. Creating, updating, and removing accounts when employees join or leave is the job of SCIM (System for Cross-domain Identity Management). Enterprise buyers increasingly ask for SSO and SCIM together.
Use the answers to three questions: who connects to you, what you’re building, and what already exists.
If you’re a B2B SaaS company, the honest answer to “SAML vs. OpenID Connect” is often both. Your own apps use OIDC internally. Your enterprise customers connect with whichever protocol their IdP prefers.
The standard way to do this is an identity broker, such as Keycloak, Auth0, Okta, or Entra ID. The broker accepts SAML or OIDC from customer IdPs and presents a single OIDC interface to your application. Your code then handles one protocol, and customer onboarding becomes configuration work.
Connecting customer IdPs, a broker, and your own applications is an integration problem as much as a security one. NextGenSoft’s software integration services cover this kind of multi-system identity work.
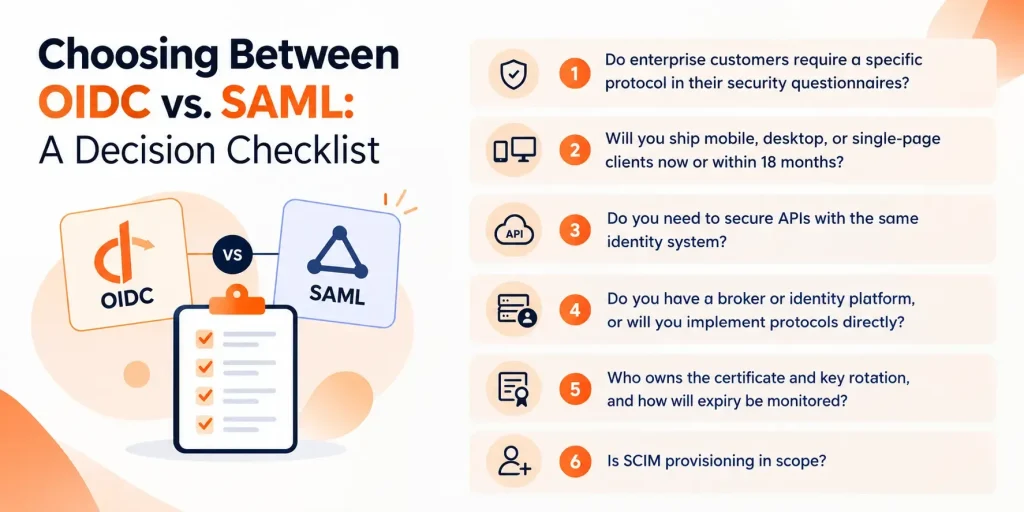
Before you commit, answer these questions:
If you answer “yes” to both enterprise requirements and mobile or API needs, plan for a broker-based architecture that supports both protocols from day one.
The OIDC vs. SAML decision isn’t about which protocol is newer. It’s about fit. SAML is the lingua franca of enterprise web SSO. OIDC is the better foundation for mobile apps, SPAs, and APIs. For most B2B products, the right architecture supports both, with a broker that keeps your application code simple.
Get the requirements right first: customer IDPs, client types, API needs, provisioning, and logout. The protocol choice usually follows from there.
Planning SSO for your product or modernizing an existing identity setup? Talk to NextGenSoft’s engineering team” about designing an authentication architecture that works for your enterprise customers and your roadmap.
1. Is OIDC more secure than SAML?
Answer: Neither protocol is inherently more secure. Both rely on signed tokens and are secure when implemented correctly. SAML’s XML signature handling is historically more error-prone, while OIDC risks come mainly from incomplete JWT validation. Library quality and correct configuration matter more than the protocol choice.
2. Can SAML and OIDC be used together?
Answer: Yes. Many organizations run both, often through an identity broker that accepts SAML or OIDC from external identity providers and issues OIDC tokens to internal applications.
3. Is SAML being replaced by OIDC?
Answer: OIDC is the default for new applications, especially mobile and API-driven ones. However, SAML remains deeply embedded in enterprise and government identity systems and is not deprecated. Expect both to coexist for years.
4. What is the difference between OAuth and OIDC?
Answer: OAuth 2.0 handles authorization: it grants an application access to resources. OIDC is built on OAuth 2.0 and adds authentication, telling the application who the user is through a signed ID token.
5. Does SAML work for mobile apps?
Answer: It can, but awkwardly. SAML depends on browser redirects and POSTs, so mobile apps must hand off to a browser and bridge the result back. OIDC with PKCE is purpose-built for native and mobile apps.
 Kushal Baldev
 is currently serving as a Technical Lead at NextGenSoft, bringing over 8.5 years of experience in software development and technology leadership. With a strong background in designing scalable systems and leading high-performing teams, Kushal has played a pivotal role in delivering innovative solutions across various domains.At NextGenSoft, he leads cross-functional teams, mentors junior developers, and collaborates with stakeholders to drive digital transformation initiatives. His dedication to continuous learning and staying updated with emerging trends has made him a valuable asset in the tech community.
We’re ISO/IEC 27001:2022 certified, ensuring your projects are executed with globally recognized security standards.

INDIA
 sales@nextgensoft.io
 +91 81284 66678

 Brijesh Shah
CEO, NextGenSoft


